Firewalld is a firewall management tool that simplifies rule configuration for Linux systems. It dynamically manages firewall rules, supports zone-based configurations, and integrates with D-Bus.
In this post I’m showing how to install Firewalld on an Amazon Linux 2 EC2 Instance. Hope you find this useful!
Installing Firewalld on Linux
1. Enable EPEL Repository:
First, install the Extra Packages for Enterprise Linux (EPEL) repository, which provides additional software packages, including Firewalld:
sudo yum install epel-release
After installation, verify that the repository has been added by running:
yum repolist | grep epel
2. Install Firewalld:
Now, install the Firewalld package using the following command:
sudo yum install -y firewalld
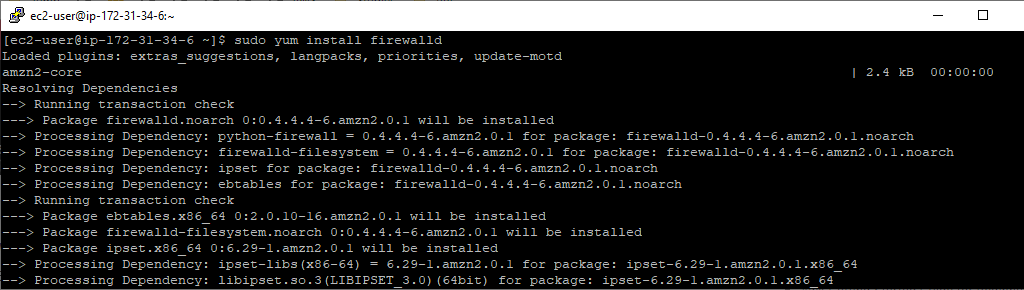
Once installed, check the package version to confirm installation:
rpm -q firewalld
3. Start and Enable Firewalld:
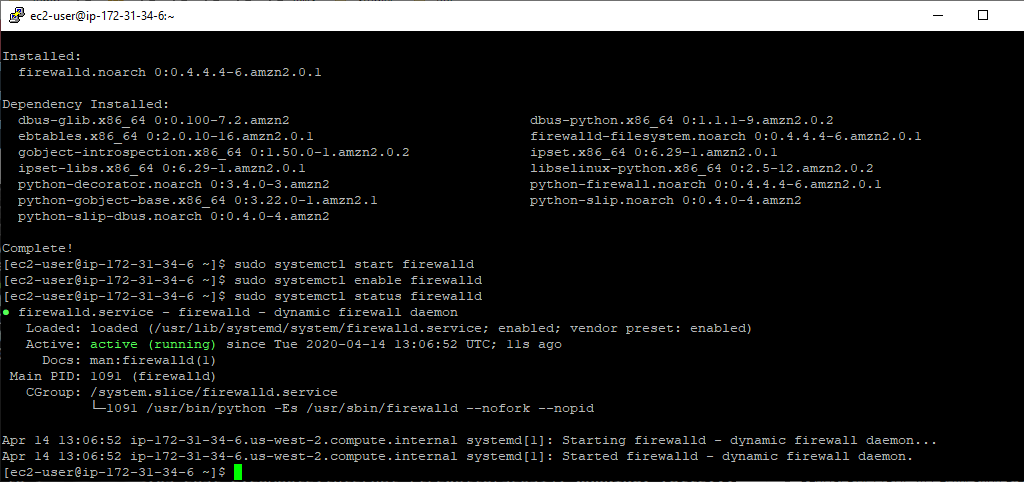
Below I’m starting the Firewalld service, enabling it to run on system boot and then checking the status of the service.
sudo systemctl start firewalld
sudo systemctl enable firewalld
sudo systemctl status firewalld
If needed, allow Firewalld through the system’s security policies:
sudo systemctl restart firewalld
4. Verify Active Rules:
Check the currently applied firewall rules using:
firewall-cmd --list-all
This command provides details on active zones, allowed services, and open ports.
Firewalld should now be installed and running. Use firewall-cmd for rule management. For advanced configurations, check the official documentation.
Related
If SQL Server is part of your day job, my current work lives over at sqldba.blog: production DBA scripts, an error library and the SSMS guide.
Leave a Reply